Business Automation Integration Checklist: Connect Systems Safely
10/09/2026
By Team Nevara | Published 9 October 2026
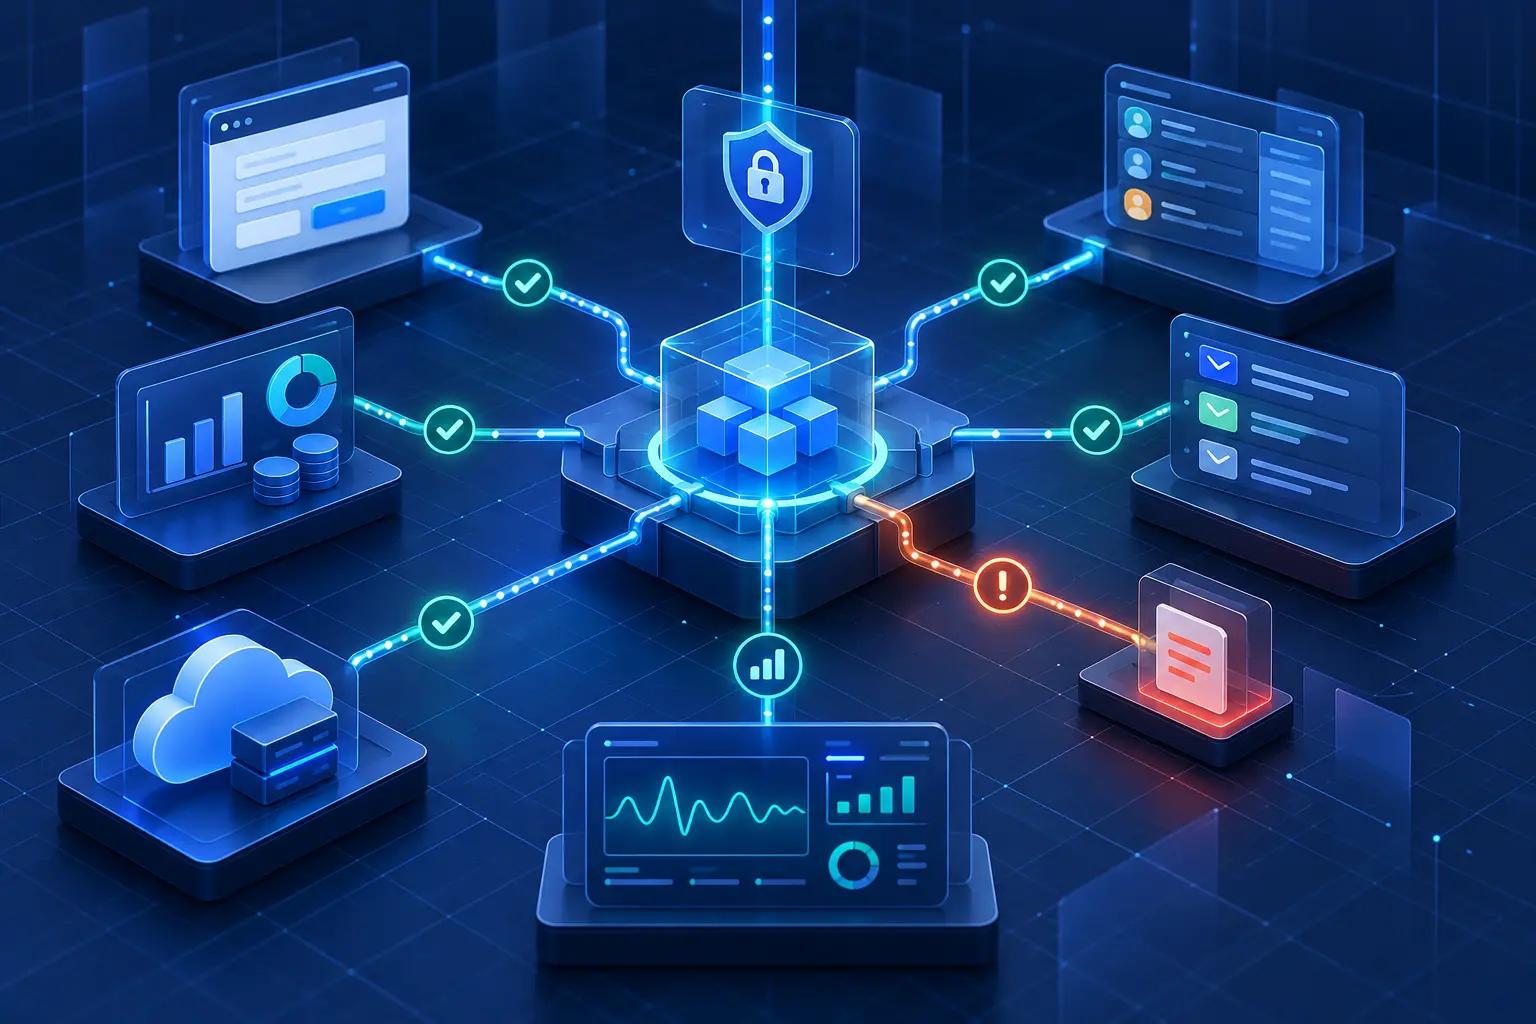
An automation is only as reliable as the systems it connects. A form may need to create a customer record, assign an owner, start a task, send a message and update finance data. Each connection introduces rules, limits and failure points that must be understood before launch.
This checklist helps business owners and delivery teams plan integrations without treating them as invisible technical plumbing. It focuses on the practical questions that affect service, risk, cost and day-to-day ownership.
Use it after you map the business process and write the automation requirements. If the tools are not yet selected, first compare no-code automation and custom software against the same requirements.
1. Define the outcome and the complete journey
Describe the business outcome before listing systems. “Connect the website to the CRM” is incomplete. A useful outcome might be: every valid enquiry creates one customer record, is assigned to the correct team within two minutes, receives an acknowledgement and appears in the follow-up queue.
Draw the journey from the first trigger to the final confirmed result. Include approvals, customer messages, documents, payments, reporting and manual steps. A connection that moves data but leaves the process unfinished is not a complete automation.
2. Name every system and its role
Create a simple inventory for each application, database, spreadsheet and external service involved.
- Business purpose and process owner
- Vendor and plan or license level
- Production account and test environment
- Data received and data sent
- Available API, webhook, export or import method
- Support contact, documentation and known limits
Do not assume a familiar product exposes every action you see in its interface. API availability often depends on the plan, account type, region or permissions.
3. Choose the source of truth for each record
Decide which system owns each important type of information. The CRM may own customer details, the finance platform may own invoice status and the operational system may own job progress. Other systems can receive copies, but ownership must be clear.
Without a source of truth, two-way updates can create conflicts. If an email address changes in two systems at the same time, the integration needs a rule for which value wins, whether the change is merged or whether a person must review it.
4. Confirm the real integration capability
Review the current API or integration documentation, then prove the specific actions the workflow needs. Check authentication, endpoints, fields, webhooks, pagination, search, file handling, rate limits and sandbox access.
The GOV.UK Service Manual explains that APIs let applications share data without sharing their internal code. Its guidance also recommends examining third-party API documentation, reliability, security, change notices and support before making a service dependent on that API.
If there is no suitable API, document the alternative and its risk. Scheduled file imports may be acceptable for daily reporting but unsuitable for real-time stock, dispatch or payment decisions. Browser automation can be fragile when interfaces change.
5. Map fields and business meaning
Create a field map that shows the source field, destination field, format, required status, transformation rule and example. Include identifiers, dates, currencies, units, status values, addresses, consent fields and document links.
Matching names do not guarantee matching meaning. “Customer,” “active,” “amount” or “completed” may mean different things in separate systems. Agree on definitions before development.
- How are existing customers matched without creating duplicates?
- Which identifier remains stable if a name or email changes?
- Which fields are mandatory in each system?
- How are time zones, currencies and decimal values handled?
- What happens to blank, invalid or unexpected values?
- Is historical data migrated, referenced or left in the old system?
6. Minimise the data that crosses the connection
Transfer only the information required for the business outcome. Extra fields increase privacy exposure, access complexity and the impact of mistakes. Record why sensitive data is needed, where it is stored, how long it is retained and who can see it.
Using open standards can make data exchange easier, reduce supplier lock-in and preserve flexibility as the service changes. This is especially useful when a business expects to replace or add systems later.
7. Design access and authentication deliberately
Use dedicated service accounts where the platform supports them. Grant only the permissions required for the integration. Keep credentials outside source code, rotate them safely and assign an owner for renewals, revoked access and staff changes.
NIST Zero Trust guidance says trust should not be granted simply because a user, device or service is on a familiar network. Authentication and authorisation should protect the actual resource. For integrations, this supports explicit identities, narrow permissions and verification for every connection.
Also decide how development and test environments access data. Real customer records should not be copied into testing by default. Use representative, safely prepared test data whenever possible.
8. Address common API security risks
The OWASP API Security Top 10 highlights risks including broken object-level authorisation, broken authentication, unrestricted resource consumption, security misconfiguration and unsafe consumption of third-party APIs. These risks should influence requirements and tests, not be added after the workflow is complete.
- Verify that each user or service can access only the correct records and actions.
- Validate incoming and outgoing data rather than trusting another system automatically.
- Protect public endpoints with authentication, rate limits and abuse controls.
- Avoid returning or logging secrets and unnecessary personal data.
- Review third-party responses before using them in a sensitive action.
- Keep an inventory of integrations, endpoints, versions and owners.
9. Plan for duplicates, retries and partial failure
Networks time out and vendors return temporary errors. A safe integration must know whether to retry, stop or request human review. Repeating a request must not accidentally create a second invoice, charge, booking or customer.
Where supported, use a stable event or idempotency key so the destination can recognise repeated attempts. Store the processing state and external record identifier. Define a maximum retry policy and move unresolved items to an exception queue rather than retrying forever.
- What if the first step succeeds but the second fails?
- Can the workflow continue later from the failed step?
- Can an operator safely replay an item?
- How is a duplicate detected and resolved?
- Which failures require customer communication?
10. Decide between real-time and scheduled transfer
Real-time processing is useful when delay affects the customer or operation. Scheduled batches may be simpler and cheaper for reporting, reconciliation or low-priority updates. State the acceptable delay and choose the simplest method that meets it.
Check volume and cost limits. APIs may cap requests per minute or charge for calls, messages, storage or data transfer. Estimate normal volume, peaks and retry traffic. A workflow that works during testing can fail under a campaign spike or month-end batch.
11. Create a visible exception process
Not every case should be forced through automation. Define which situations stop for human review, who owns the queue, what information they receive and how the corrected result returns to the process.
Common exceptions include missing customer identifiers, conflicting records, unsupported files, unusual prices, failed consent checks, rejected payments and actions above an approval limit.
12. Make the integration observable
A success message from the first system does not prove the business outcome completed. Monitor the complete journey.
- Number of items started, completed, rejected and waiting
- Processing time from trigger to confirmed result
- Failures by system, step and reason
- Retry volume and duplicate prevention
- Data-quality exceptions and manual corrections
- API response time, rate-limit warnings and authentication failures
Alerts must lead to an owner and action. A dashboard nobody checks does not protect the process. Set thresholds for urgent failures and a review schedule for slower trends.
Our guide to monitoring business automation after launch explains how to combine technical signals with outcome measures and an exception queue.
13. Agree how changes will be managed
Vendors change fields, authentication, limits and API versions. Your own team changes forms, statuses and business rules. Record dependencies and decide who reviews release notices, tests updates and approves production changes.
Use versioned configurations and separate test credentials. Keep a rollback or disable option for material changes. If an integration controls a customer-facing or financial action, avoid unreviewed changes directly in production.
14. Test the whole process with realistic cases
Test normal, boundary and failure cases across every connected system. Confirm both the system result and the business result. A record appearing in the CRM is not enough if it has the wrong owner, missing consent or no follow-up task.
- Valid new record and valid existing record
- Missing, malformed and duplicate data
- Permission denied and expired credential
- Timeout, rate limit and unavailable vendor
- File too large or unsupported format
- Partial completion and safe replay
- Audit trail, alert and manual recovery
Run these checks inside a controlled automation pilot with defined acceptance criteria before full rollout.
An illustrative example
Consider a fictional property maintenance company connecting a website form, CRM, scheduling tool and accounting system. This example is illustrative and is not a Nevara client result.
The enquiry first creates or matches a CRM contact. A valid service request creates a job and assigns a coordinator. Scheduling happens only after postcode and service checks. A completed visit can request an invoice, but a price change above the agreed limit stops for approval. Each system returns its record identifier, while failed or conflicting items enter one visible review queue.
The valuable design is not simply four systems connected by arrows. It is the agreed ownership, validation, security, exception handling and evidence that the final business action occurred.
Frequently asked questions
What is the first thing to check before integrating two systems?
Confirm the business outcome and the exact capabilities available in both systems. Check current documentation, account permissions and plan limits before assuming the connection is possible.
Should integrations update data in both directions?
Only when there is a clear ownership and conflict rule. One-way transfer is often easier to control. Two-way sync can be appropriate, but it needs stable identifiers, loop prevention and a defined source of truth.
Is a native app integration automatically reliable?
No. A native connector can reduce implementation work, but its supported fields, triggers, delays, error handling, security and monitoring still need to match the process.
How should integration errors be handled?
Classify errors as temporary, permanent or requiring review. Use limited safe retries for temporary failures, prevent duplicates and route unresolved items to an owned exception queue with enough context to act.
How often should integrations be reviewed?
Review operational health continuously through alerts and scheduled reports. Review business fit, access, vendor changes, costs and data handling at planned intervals and whenever the process or a connected product changes.
Turn the checklist into an owned integration plan
For every connection, document the outcome, system owners, source of truth, data map, authentication, limits, failure policy, monitoring, test cases and change owner. This creates a buildable plan and makes supplier proposals easier to compare.
Nevara Solutions designs and delivers business automation, custom web platforms, mobile applications and SaaS products with the required integrations and operational controls. Explore our development services or contact us to turn a process and system inventory into a practical integration plan.
